One knowledge workspace
Collaboration, files and governed records share a workspace with controlled ingestion and search.
Les descriptions produit actualisées et les dossiers techniques sont maintenus en anglais.
IA souveraine et agents
A private workspace for knowledge, collaboration and governed AI.
Documents, search and AI work are fragmented. Your team needs to explain where information goes, who can use it and which actions require review.
CIOs, knowledge owners and AI-platform leads
Active development · local reference
Explore the reasoning
Choose one organisation and an approved set of information. Identify access rules, hosting constraints and the model route to evaluate.
The decision behind the system
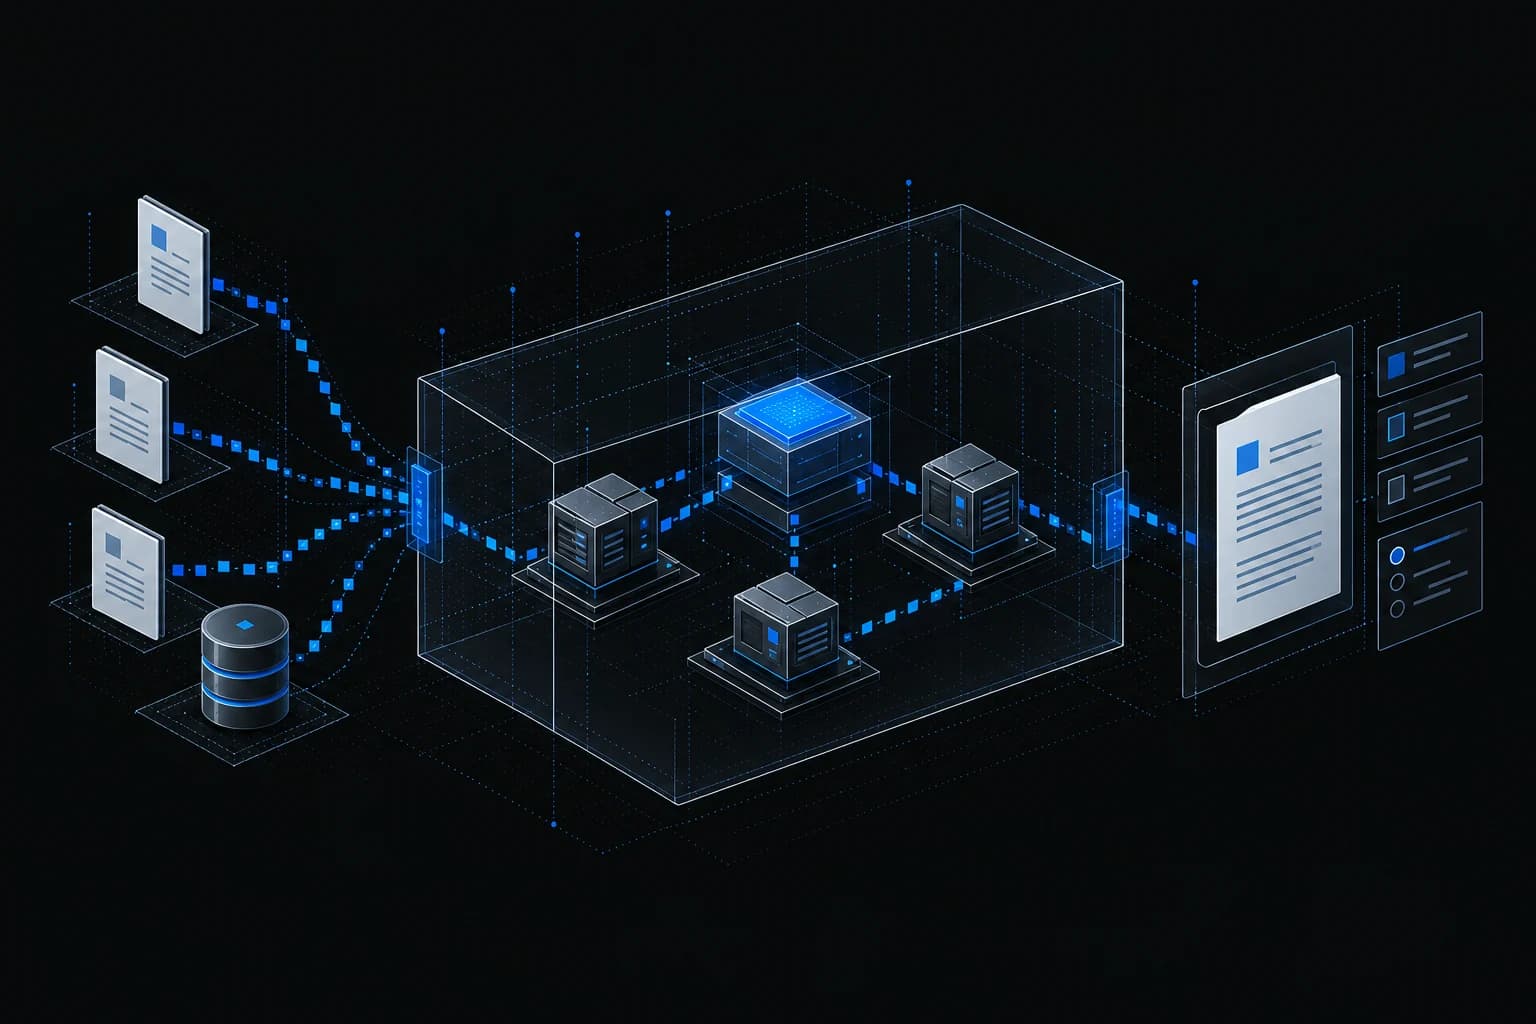
Bring files, records, search and AI-assisted work into one organisation-controlled workspace, with identity, policy and audit boundaries designed together.
Sovereign Fabric explores the knowledge and control workspace. Athena focuses on departmental agent work; Techne focuses on creative workflows. Their inclusion here does not imply an integrated suite.
Collaboration, files and governed records share a workspace with controlled ingestion and search.
Separate model-assisted work from identity, policy and audit decisions. Examine the route that data and requests take.
Inspect backup, status and administrative surfaces alongside the application. Remote deployment and release remain separate work.
Choose one organisation and an approved set of information. Identify access rules, hosting constraints and the model route to evaluate.
Follow approved documents and records into the workspace. Examine ingestion, search and the information available to each identity.
Explore retrieval and drafting while keeping model output separate from policy decisions and permission to act.
Inspect audit, administration, backup and status boundaries. Source configuration alone does not establish residency or operational isolation.
Workspace, file, record, ingestion, search and AI source surfaces.
No hosted production service, customer deployment or operational data-residency result is established.
Review a single-organisation use case, data boundary and model-hosting constraints before a scoped evaluation. This is an implementation reference, not a hosted offer.
These are source and research records. Illustrative examples do not establish deployment, integration, certification or customer outcomes.
Pont métier ↔ technologie · A private workspace for knowledge, collaboration and governed AI.
Sovereign Fabric explores the knowledge and control workspace. Athena focuses on departmental agent work; Techne focuses on creative workflows. Their inclusion here does not imply an integrated suite.
Il s'agit d'une interprétation du portefeuille et des sources, et non d'une affirmation de client, déploiement, certification ou résultat.
Documents, search and AI work are fragmented. Your team needs to explain where information goes, who can use it and which actions require review.
Choose one organisation and an approved set of information. Identify access rules, hosting constraints and the model route to evaluate. Inspect audit, administration, backup and status boundaries. Source configuration alone does not establish residency or operational isolation.
Collaboration, files and governed records share a workspace with controlled ingestion and search. Separate model-assisted work from identity, policy and audit decisions. Examine the route that data and requests take. Inspect backup, status and administrative surfaces alongside the application. Remote deployment and release remain separate work.
Inspect audit, administration, backup and status boundaries. Source configuration alone does not establish residency or operational isolation.
Preuves issues du code source
A single-organisation workspace implementation joining collaboration, files, governed records, controlled ingestion, search and AI with identity, policy, audit and operational surfaces.
Le relevé technique détaillé est maintenu en anglais.
Les preuves du dépôt ne constituent pas des preuves client, de déploiement, de certification ou de résultats.
Work with Hyperion
An information and model-route review, with evaluation criteria and the integration work needed for your use case.
Bring a short description of your situation, constraints and decision. We agree the scope, responsibilities and quote before work begins.